Introduction to Bad Bots
Bad bots are automated software programs designed to perform malicious or harmful tasks on the internet. These activities threaten organizations and individuals, compromise security, and erode trust.
Bad bots typically exploit vulnerabilities in online systems and applications for for financial gain or other malicious goals.
Bad bots can be used to launch attacks on almost every industry. That said, industries with high volumes of financial transactions, such as e-commerce and financial services.
Types of Bad Bots
The bad bot landscape keeps evolving with new variations and attack methods. These are the most common types:
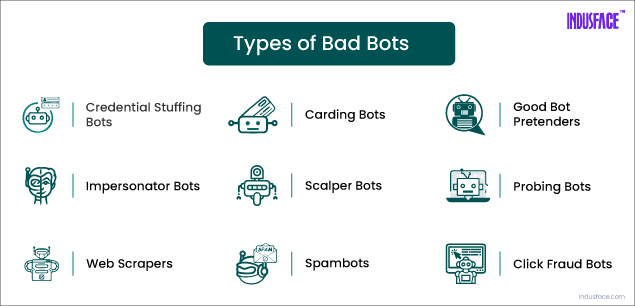
1. Credential Stuffing/Account Takeover Bots
These bots automate the process of testing large numbers of stolen usernames and passwords on various websites to gain unauthorized access to user accounts. They exploit the common practice of password reuse across multiple online services. Once a valid combination is found, the bot can access the account for malicious purposes such as identity theft, fraud, or further credential harvesting.
Credential stuffing bots are dangerous as they give bots access to the systems directly. These could be more dangerous where there are also privilege-escalation vulnerabilities and a user account that is compromised is potentially used to access the admin accounts.
Learn more about account takeover attacks and these tips to prevent credential stuffing attacks.
2. Carding Bots
Carding bots test stolen credit card details for validity and use them for fraudulent purchases. They automatically enter card numbers, expiration dates, and CVV codes on e-commerce checkout pages, often with small transactions that go unnoticed.
Carding bots use techniques such as spoofing, session hijacking, IP rotation, and automated CAPTCHA solving to evade fraud detection systems.
Gain more insights into carding attacks and preventive measures.
3. Good Bot Pretenders
Bad bots can change their user agent strings to copy well-known crawlers such as Googlebot or Bingbot. Security rules that allow known good bots then let them through while blocking unknown traffic.
This tactic now extends to AI crawlers. Scrapers increasingly pose as GPTBot, ClaudeBot, or PerplexityBot to collect content from sites that allow those crawlers.
Bad bots may also spoof their IP addresses to appear to come from legitimate hosting providers or data centers. This helps them avoid IP-based blocking and rate limiting. To tell real crawlers from fakes, check the request’s IP against the operator’s published IP ranges and confirm it with a reverse DNS lookup. See how to set WAF policies for AI crawlers that go beyond simple blocking.
4. Impersonator Bots
Impersonator bots mimic human behavior to impersonate legitimate users on websites, social media platforms, or messaging apps. They may create fake accounts, interact with other users, or engage in automated conversations.
Impersonator bots can be used for various purposes, including spreading misinformation, manipulating online discussions, or influencing public opinion.
5. Scalper Bots
Scalper bots are used to automate the purchase of limited-release or high-demand products from e-commerce websites, ticketing platforms, or online auctions. They work by repeatedly sending requests to purchase products as soon as they become available, often bypassing rate limits and security measures.
Scalper bots can quickly deplete inventory and resell products at inflated prices on secondary markets.
6. Probing Bots
Probing bots are programmed to scan websites, servers, or network devices for vulnerabilities. They can exploit known security flaws to gain unauthorized access, inject malicious code, or steal sensitive data.
These bots are typically used to find vulnerabilities first and then use other bots to exploit the vulnerabilities.
7. Web Scrapers
These bots are designed to automatically extract data from websites, often without permission. They work by sending HTTP requests to target websites, parsing the HTML content, and extracting specific information such as product details, prices, or contact information.
Web scrapers can be used for legitimate purposes, but when used without authorization, they can drain website resources and more importantly steal intellectual property and be used to gain unfair competitive advantage. They could also be used in conjunction with other bots such as scalper bots to cause inventory stock outs.
8. API Abuse Bots
Attackers increasingly skip the website and go straight to the APIs behind it. In 2025, 27% of bot attacks targeted APIs directly. These bots often use valid authentication and well-formed requests, so their traffic looks legitimate. They exploit business logic, extract sensitive data, and manipulate workflows at scale. Protecting against them requires strong API security alongside bot detection.
9. Spambots
Spambots are bots that generate and distribute spam emails, social media messages, or comments. They often operate by harvesting email addresses or social media profiles from public sources or compromised databases.
Spambots can flood inboxes and social media feeds with unsolicited messages promoting scams, phishing links, or fake products/services.
10. Click Fraud Bots
Click fraud bots simulate human clicks on online advertisements, pay-per-click ads, or affiliate links to generate revenue for bot operators while defrauding advertisers.
They can inflate website traffic and click counts artificially, leading to inaccurate analytics data and wasted advertising budgets. Click fraud bots may use proxies or distributed networks to evade detection.
What Is Bot Fraud?
Bot fraud is any fraudulent activity carried out by automated bots for financial gain. It includes account takeover, carding, fake account creation, click fraud, scalping, gift card abuse, and fake promotional sign-ups. Bot fraud scales in a way human fraud cannot. One attacker can run thousands of attempts per minute across many accounts, IP addresses, and devices.
Bot fraud is hard to spot because each individual request can look normal. The fraud shows up in the pattern, such as many accounts sharing one device fingerprint, or checkout attempts arriving faster than any human could type.
The Impact of Bad Bots
Overall, the impacts of bad bot attacks can be far-reaching and multifaceted, affecting not only the targeted organization but also its customers, partners, and the broader digital ecosystem. Here are some of the most important impacts:
1. Financial Losses
Bad bot attacks can result in significant financial losses for businesses due to stolen revenue, fraudulent transactions, increased operational costs for mitigating the attack, and potential fines or legal fees resulting from regulatory violations.
Scalping operations use bots, multiple accounts, and proxy networks to get around purchase limits and resell tickets and limited products at inflated prices. Businesses lose revenue and customer goodwill, and in the US, regulators have stepped up enforcement under the BOTS Act.
2. Damage to Reputation
Bad bot attacks can damage the reputation and trustworthiness of businesses and organizations. Customers may lose confidence in the security of the platform, leading to decreased user engagement, customer churn, and long-term damage to brand loyalty.
Social media platforms show how this plays out. Twitter (now X) faced sustained criticism for failing to control bot and fake accounts used to amplify political propaganda and spread misleading information during election campaigns. This raised public concern about the integrity of online discussion.
3. Data Breaches
Bad bot attacks can lead to data breaches that expose customer data, payment details, intellectual property, and trade secrets. The result can include regulatory penalties, legal liability, and reputational damage.
Many breaches start with open vulnerabilities such as SQL injection in a website or API. Attackers often use probing bots to find these weaknesses at scale before exploiting them. Credential stuffing bots create a second path to breaches by taking over accounts with access to sensitive data.
4. Disruption of Operations
Bad bot attacks can disrupt the normal functioning of websites, applications, and online services, leading to downtime, degraded performance, and loss of productivity for users and employees. This can have cascading effects on business operations and revenue generation.
Bot-driven DDoS attack is the most common method to disrupt operations. The WireX botnet, discovered in 2017, used a network of compromised Android devices to launch DDoS attacks against content delivery networks and content providers.
5. Negative SEO Impact
Bad bots engaging in web scraping or content scraping can negatively impact a website’s search engine optimization (SEO) efforts by duplicating content, diluting keyword relevance, and causing indexing issues. This can result in decreased search engine rankings, reduced organic traffic, and diminished online visibility.
6. Wasted Resources
Bad bot attacks consume valuable server resources, bandwidth, and computing power, leading to increased hosting costs, slower website performance, and reduced scalability. This can strain IT infrastructure and impede the delivery of services to legitimate users.
7. Legal and Regulatory Consequences
Bad bot attacks may violate laws, regulations, or industry standards related to data privacy, cybersecurity, and consumer protection. Organizations found to be non-compliant may face regulatory investigations, fines, and legal action from affected parties or regulatory authorities.
8. Loss of Competitive Advantage
Bad bot attacks targeting competitors can undermine their competitive advantage by stealing intellectual property, proprietary data, or business intelligence. This can lead to loss of market share, decreased profitability, and weakened competitiveness in the marketplace.
9. Social and Ethical Implications
Bad bot attacks can have broader social and ethical implications, including the spread of misinformation, manipulation of public opinion, and erosion of trust in digital platforms. This can undermine the integrity of democratic processes, public discourse, and societal norms.
Detection and Prevention Techniques
Detecting and stopping bad bots is essential to protect applications, data, and users. Attackers use bots for credential stuffing, scraping, spam, fraud, and DDoS attacks. AI-driven bots make detection harder because they change their behavior to avoid known patterns. These are the key techniques.
Detection Techniques for Bad Bots
- CAPTCHA Challenges – Completely Automated Public Turing tests to tell Computers and Humans Apart (CAPTCHAs) are widely used to differentiate between real users and bots. By requiring users to solve puzzles, image recognition tasks, or one-click verifications, CAPTCHAs disrupt automated scripts that cannot pass these challenges. Learn how a CAPTCHA works.
- Honeypots – These are hidden form fields or deceptive pages designed to detect and trap malicious bots. Since legitimate users cannot see or interact with honeypots, any engagement with these elements signals bot activity, allowing organizations to block such requests.
- Behavioral Analysis – Advanced bot detection systems analyze user behavior, such as mouse movements, keystroke patterns, navigation speed, and interaction frequency. Bots often exhibit unnatural behaviors—such as excessively fast clicks or lack of cursor movement—that can be flagged as suspicious.
- Traffic Pattern Monitoring – Identifying anomalies in traffic patterns, such as a sudden spike in requests from a single IP or repeated logins in quick succession, helps detect bot-driven attacks. Machine learning models can refine detection by analyzing historical data and recognizing evolving bot behaviors.
Prevention Techniques for Bad Bots
- User Agent and IP Reputation Analysis – Security tools can block known bad user agents and IP addresses associated with botnets or malicious activities. A continuously updated reputation database ensures that threats are proactively mitigated.
- Multi-Factor Authentication (MFA) – Requiring users to verify their identity through an additional authentication step, such as SMS codes or biometric verification, significantly reduces the risk of automated login attacks.
- JavaScript and Device Fingerprinting – Advanced bot mitigation tools use JavaScript-based detection and device fingerprinting to assess browser integrity, screen resolution, installed plugins, and other device attributes. Bots that fail these validation checks are blocked.
- Web Application Firewall (WAF) with Bot Mitigation –With bot mitigation capabilities, WAFs use behavioral analysis, rate limiting, and machine learning to differentiate between real users and automated threats. AI-assisted WAFs continuously learn from traffic patterns, improving their ability to detect and mitigate evolving bot threats with higher accuracy.
Key Ways WAFs Prevent Bot Attacks
- Traffic Filtering & Anomaly Detection – Monitors incoming requests to detect unusual behavior, such as rapid login attempts or high-frequency API calls.
- Bot Signature & Behavioral Analysis – Identifies bots based on known attack patterns, header inconsistencies, and non-human interaction behaviors.
- Rate Limiting – Restricts excessive requests from a single source to prevent credential stuffing, scraping, and brute-force attempts.
- DDoS Protection – Identifies and blocks botnets attempting to overwhelm the system with fake traffic.
- Custom Security Rules – Enables businesses to fine-tune bot defense based on risk level, traffic intent, and industry-specific threats.
- Advanced Bot Control – Uses JavaScript challenges, browser fingerprinting, and CAPTCHA enforcement to detect stealthy bots trying to bypass detection.
- Threat Intelligence – Leverages real-time data from global security networks to proactively block emerging bot threats.
To understand more about how WAFs function as a critical security layer, check out our detailed blog on How Does a WAF Work?.To compare solutions, see our list of top bot management software.
Regulatory and Legal Considerations
The legal landscape around bad bots is complex and varies by country and industry. If your company suspects bot activity, these laws and regulations may shape your next steps.
Computer Fraud and Abuse Act (CFAA)
In the United States, the Computer Fraud and Abuse Act (CFAA) is a federal law that prohibits unauthorized access to computer systems and networks. Bad bots that gain access to protected computer systems without authorization may be subject to prosecution under the CFAA. The CFAA has been used in cases involving unauthorized access, hacking, and data breaches perpetrated by bad actors, including bot operators.
Data Protection and Privacy Regulations
Bad bots that collect personal or sensitive information from websites without consent may violate data protection and privacy regulations, such as the GDPR (General Data Protection Regulation) in the European Union or the CCPA (California Consumer Privacy Act) in the United States. These regulations impose strict requirements on the collection, processing, and handling of personal data and may subject bad bot operators to fines, penalties, and legal liabilities for non-compliance.
Copyright and Intellectual Property Laws
Bad bots that scrape copyrighted content or proprietary information from websites without authorization may infringe on the intellectual property rights of the website owners. Copyright laws protect original works of authorship, including text, images, and multimedia content, from unauthorized reproduction or distribution.
Anti-Competitive Practices and Unfair Competition Laws
Bad bots that engage in anti-competitive practices, such as price scraping, market manipulation, or deceptive advertising, may violate anti-trust laws and unfair competition statutes. Companies harmed by these practices may pursue legal action under anti-trust laws, consumer protection laws, or unfair competition statutes to seek damages, injunctive relief, or other remedies.
Botnet Regulation and Cybersecurity Laws
Botnets, networks of compromised computers or devices controlled by malicious actors, are subject to regulation under cybersecurity laws and regulations aimed at preventing cyber-attacks, data breaches, and other malicious activities. Governments may enact legislation and regulatory frameworks to combat botnets, enhance cybersecurity, and protect critical infrastructure from cyber threats posed by bad bots.
Check out the 10 Botnet Detection and Removal Best Practices
Case Studies of Bad Bot Attacks Blocked by AppTrana WAAP
Botnet-Driven Low Rate DDoS attack on a Fortune 500 Company
A Fortune 500 commodities trader was hit by a botnet driven DDoS attack from 8 million+ IPs where the attack traffic was 14000X the usual traffic.
Learn how AppTrana WAAP kept the site at 100% availability. Read the complete case study here.
Carding Bot Attack on a US Jewellery Retailer
A large US jeweller was facing a lot of card cracking attacks and the attackers could even place up to fifteen high ticket orders with an attack.
Learn how 16,000 such attacks were mitigated 100% within a few hours. Download the case study here.
Future Trends and Emerging Threats
Bad bots will keep getting more sophisticated and diverse, and the contest between attackers and defenders will keep speeding up. These are the most important emerging threats.
1. AI-Driven Bots and AI Agents
AI is changing both the volume and the nature of bot traffic. AI agents have emerged as a third category of traffic, alongside traditional good bots and bad bots. AI-driven bots copy human behavior closely, change their tactics when blocked, and produce realistic text for spam and fake accounts. The line between a legitimate AI agent and a malicious bot is getting harder to see, so security teams must judge the intent of traffic as well as its identity.
2. Botnet-as-a-Service
DDoS as a service platforms are already plentiful on the Dark Web. These platforms are evolving to become botnet-as-a-service (BaaS) platforms. While compute power is already cheap, with the emergence of AI and LLM, hackers can now easily rent let’s say an account-take-over bot or a scalping bot.
This will make it easier for novice hackers to orchestrate sophisticated attacks without specialized technical knowledge.
3. IoT Botnets
Mirai botnet was among the most notorious IoT botnets and this was discovered way back in 2016. That said, nowadays even the most rudimentary electrical devices such as bulbs are IoT enabled. This is a ripe opportunity for hackers because of widespread adoption, lack of security controls, and always-on connectivity. Once infected, these devices maybe used to launch large-scale DDoS attacks, distribute malware, or carry out other malicious activities.
4. API-First Attacks
As businesses move core functions to APIs, bots follow. API attacks bypass the front end entirely, and their well-formed requests make them hard to spot with traditional web filters. Business logic abuse and data leakage through APIs will keep growing as a bot threat.
Conclusion
According to our study, state of application security, bot attacks have increased by 147% in the last year and nine out of ten sites are hit by bot attacks every single day.
Bad bots are growing in volume, and AI makes them faster, more adaptive, and harder to tell apart from real users. Bots-as-a-service platforms put these capabilities in the hands of anyone. Security teams need layered defenses that combine behavioral analysis, API protection, and expert oversight. AppTrana WAAP provides AI-assisted bot protection with expert-backed operations built in.