Node2Shell (CVE-2026-111497): Node.js Brotli RCE
On October 21, 2026, Node.js fixed CVE-2026-111497, now known as Node2Shell. The bug is in its bundled Brotli…
89 articles
On October 21, 2026, Node.js fixed CVE-2026-111497, now known as Node2Shell. The bug is in its bundled Brotli…
PHP2Shell abuses PHP’s session upload progress feature. Learn the signs of exploitation, php.ini hardening steps, and how AppTrana…
Microsoft’s October 2026 Patch Tuesday fixes 1,413 vulnerabilities, including exploited Windows Shell zero-day CVE-2026-96951. See AppTrana coverage.
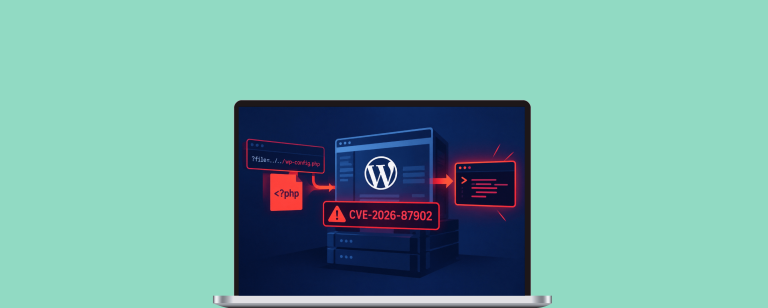
CVE-2026-87902 is a critical WordPress Core RCE flaw, exploited within hours of patch. See affected versions, exploitation flow,…
Next.js CVE-2026-94545 (CVSS 9.5) enables RCE through next/og SVG image generation. Learn affected versions, the Satori root cause,…
ShinyHunters now bypasses WAF rules to exploit Oracle PeopleSoft CVE-2026-35273. See the new attack chain, detection steps, and…
cPanel disclosed a critical EmailTrack flaw letting standard mail accounts reach root access. Check affected versions, patch links,…
Critical Langflow RCE (CVE-2026-0768) is under active exploitation via the validate endpoint. Learn the impact, IOCs, and how…
CVE-2026-55040, a critical SharePoint authentication bypass, is now being actively exploited. A proof-of-concept went public on August 11.…
CVE-2026-9198 lets attackers chain two Langflow API endpoints for unauthenticated RCE. CISA confirms active exploitation. See fixes and…
CVE-2026-58048 lets low-privilege cPanel accounts escalate to root database access via a public PoC. Explore risk details and…
Oracle's largest-ever CPU patches critical unauthenticated flaws in PeopleSoft, WebLogic, and E-Business Suite. See AppTrana's coverage for each.