WordPress CVE-2026-87902: Unauthenticated RCE Exploited Within Hours
CVE-2026-87902 is a critical WordPress Core RCE flaw, exploited within hours of patch. See affected versions, exploitation flow,…
15 articles
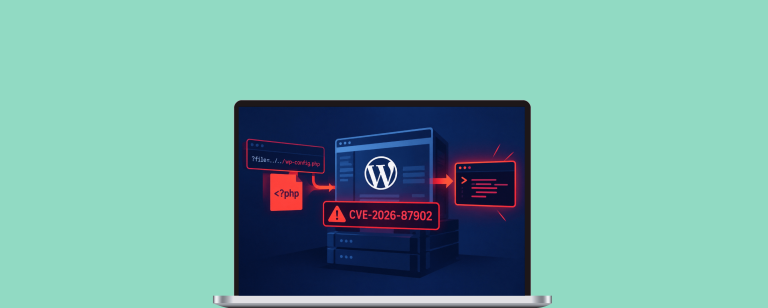
CVE-2026-87902 is a critical WordPress Core RCE flaw, exploited within hours of patch. See affected versions, exploitation flow,…
Next.js CVE-2026-94545 (CVSS 9.5) enables RCE through next/og SVG image generation. Learn affected versions, the Satori root cause,…
Quantum computers could very soon undermine the public-key cryptography that secures financial transactions, health records, and other sensitive…

CVE-2026-9198 lets attackers chain two Langflow API endpoints for unauthenticated RCE. CISA confirms active exploitation. See fixes and…

CVE-2026-58048 lets low-privilege cPanel accounts escalate to root database access via a public PoC. Explore risk details and…

Examine the functionality of the best API security tools, along with their key features, reviews, ratings, and insights…
AppTrana WAAP helps meet RBI Digital Payment Security Controls, including Clause 8 risk assessment, Clause 15 WAF/DDoS, and…
By identifying & cataloging in-use APIs, API discovery enables organizations to assess security risks associated with each API…
Learn how 5 high-margin AppSec bundles—vulnerability scans, WAAP, bot protection, pen tests and secure hosting—help MSPs grow revenue…
WAF for healthcare needs to cover APIs, legacy systems, & HIPAA compliance. Here are the 6 capabilities that…
Discover the key questions to ask your WAF provider to ensure security, cost-effectiveness, and real-time protection before choosing…
WAAP (Web Application and API Protection) is a security solution that defends web apps and APIs against threats,…