PHP2Shell (CVE-2026-109618 & CVE-2026-109619): Pre-Auth RCE in PHP Core Puts Web Servers at Risk
PHP2Shell abuses PHP’s session upload progress feature. Learn the signs of exploitation, php.ini hardening steps, and how AppTrana…
27 articles
PHP2Shell abuses PHP’s session upload progress feature. Learn the signs of exploitation, php.ini hardening steps, and how AppTrana…
cPanel disclosed a critical EmailTrack flaw letting standard mail accounts reach root access. Check affected versions, patch links,…
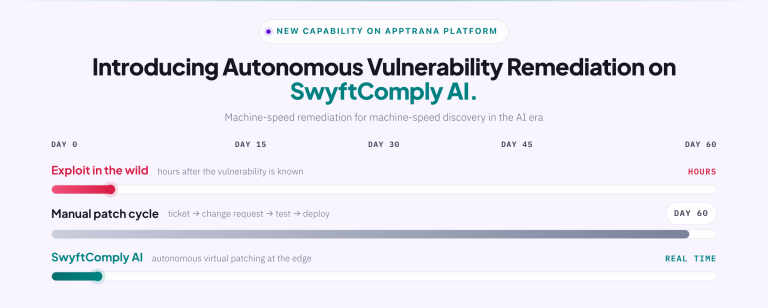
SwyftComply AI closes the vulnerability discovery-to-protection gap before attackers exploit it. Autonomous protection, expert-verified, audit-ready.
Critical Langflow RCE (CVE-2026-0768) is under active exploitation via the validate endpoint. Learn the impact, IOCs, and how…
CVE-2026-55040, a critical SharePoint authentication bypass, is now being actively exploited. A proof-of-concept went public on August 11.…
CVE-2026-9198 lets attackers chain two Langflow API endpoints for unauthenticated RCE. CISA confirms active exploitation. See fixes and…
CVE-2026-58048 lets low-privilege cPanel accounts escalate to root database access via a public PoC. Explore risk details and…
Critical unauthenticated RCE vulnerability CVE-2026-6875 hits ServiceNow via a GlideRecord sandbox escape. Attackers are already exploiting unpatched instances.
WP2Shell chains CVE-2026-60137 and CVE-2026-63030 for unauthenticated RCE on WordPress Core. Patch to 6.8.6, 6.9.5, or 7.0.2 now,…
Run 6 quick checks to find exposed API endpoints, broken auth, and data leaks before attackers do. See…
CERT-In's AI security blueprint sets a 12-hour window for internet-facing vulnerabilities. See what it requires and how AppTrana…
Discover the pros and cons of Cloudflare WAF and the top 5 Cloudflare alternatives, including AppTrana, Akamai, Imperva,…