Guardians of the Enterprise — Insights from leading cyber experts.

Listen Now →
Live Intelligence

Security Intelligence for Modern Threats

Real-time vulnerability analysis, threat intelligence, and expert insights to protect your web, API and AI agents from emerging attacks.
API vulnerability exploitation jumped 181% in 2025  accelerated by LLM-assisted tooling.
Loading…
PHP2Shell (CVE-2026-109618 & CVE-2026-109619): Pre-Auth RCE in PHP Core Puts Web Servers at Risk

PHP2Shell (CVE-2026-109618 & CVE-2026-109619): Pre-Auth RCE in PHP Core Puts Web Servers at Risk

PHP2Shell abuses PHP’s session upload progress feature. Learn the signs of exploitation, php.ini hardening steps, and how AppTrana…
Windows Shell Zero-Day and 1,413 Fixes: Microsoft October 2026 Security Update

Windows Shell Zero-Day and 1,413 Fixes: Microsoft October 2026 Security Update

Microsoft’s October 2026 Patch Tuesday fixes 1,413 vulnerabilities, including exploited Windows Shell zero-day CVE-2026-96951. See AppTrana coverage.
WordPress CVE-2026-87902: Unauthenticated RCE Exploited Within Hours

WordPress CVE-2026-87902: Unauthenticated RCE Exploited Within Hours

CVE-2026-87902 is a critical WordPress Core RCE flaw, exploited within hours of patch. See affected versions, exploitation flow,…
Next.js CVE-2026-94545: Critical ImageResponse Vulnerability Enables RCE via SVG

Next.js CVE-2026-94545: Critical ImageResponse Vulnerability Enables RCE via SVG

Next.js CVE-2026-94545 (CVSS 9.5) enables RCE through next/og SVG image generation. Learn affected versions, the Satori root cause,…
<em>CVE-2026-35273</em>: ShinyHunters Resumes Oracle PeopleSoft Exploitation with WAF Bypass

CVE-2026-35273: ShinyHunters Resumes Oracle PeopleSoft Exploitation with WAF Bypass

ShinyHunters now bypasses WAF rules to exploit Oracle PeopleSoft CVE-2026-35273. See the new attack chain, detection steps, and…
AppTrana Adds Post-Quantum Cryptography Support with X25519MLKEM768

AppTrana Adds Post-Quantum Cryptography Support with X25519MLKEM768

Quantum computers could very soon undermine the public-key cryptography that secures financial transactions, health records, and other sensitive…
CVE-2026-67401: SQL Injection in cPanel’s EmailTrack Puts Shared Hosting Environments at Risk

CVE-2026-67401: SQL Injection in cPanel’s EmailTrack Puts Shared Hosting Environments at Risk

cPanel disclosed a critical EmailTrack flaw letting standard mail accounts reach root access. Check affected versions, patch links,…
Indusface WAS AI-Assisted Pentest: Comprehensive Vulnerability Assessment Across Web, API and AI Apps

Indusface WAS AI-Assisted Pentest: Comprehensive Vulnerability Assessment Across Web, API and AI Apps

Manual pentesting samples your risk. Indusface WAS AI Pentest tests every endpoint, role, and workflow, with expert validation…
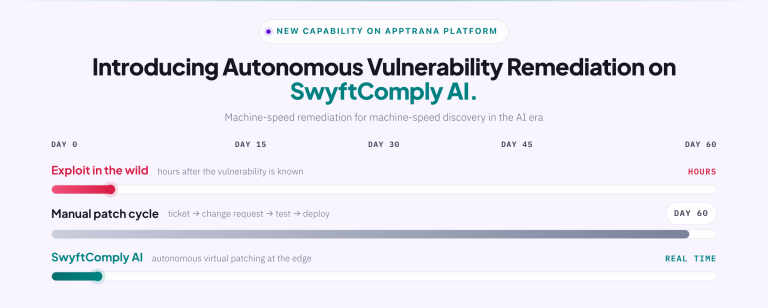
SwyftComply AI: How We Turn Vulnerability Flood Into Audit-Ready Protection

SwyftComply AI: How We Turn Vulnerability Flood Into Audit-Ready Protection

SwyftComply AI closes the vulnerability discovery-to-protection gap before attackers exploit it. Autonomous protection, expert-verified, audit-ready.
CVE-2026-0768: Critical RCE in Langflow AI Agent Builder

CVE-2026-0768: Critical RCE in Langflow AI Agent Builder

Critical Langflow RCE (CVE-2026-0768) is under active exploitation via the validate endpoint. Learn the impact, IOCs, and how…
SharePoint CVE-2026-55040 Actively Exploited: AI-Discovered RCE Chain

SharePoint CVE-2026-55040 Actively Exploited: AI-Discovered RCE Chain

CVE-2026-55040, a critical SharePoint authentication bypass, is now being actively exploited. A proof-of-concept went public on August 11.…
CVE-2026-9198: Critical Langflow RCE Under Active Exploitation

CVE-2026-9198: Critical Langflow RCE Under Active Exploitation

CVE-2026-9198 lets attackers chain two Langflow API endpoints for unauthenticated RCE. CISA confirms active exploitation. See fixes and…

DDoS attacks on APIs were 675% higher  than on websites in 2025. API gateways handle routing, not adversarial security.

Get weekly threat intelligence

Join 51,000+ security leaders receiving real-time alerts and analysis