WordPress CVE-2026-87902: Unauthenticated RCE Exploited Within Hours
CVE-2026-87902 is a critical WordPress Core RCE flaw, exploited within hours of patch. See affected versions, exploitation flow,…
19 articles
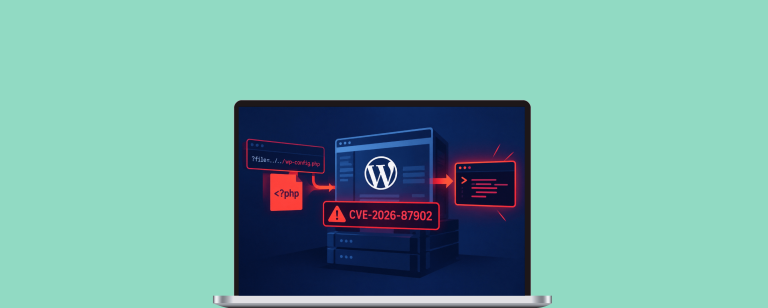
CVE-2026-87902 is a critical WordPress Core RCE flaw, exploited within hours of patch. See affected versions, exploitation flow,…

CVE-2026-55040, a critical SharePoint authentication bypass, is now being actively exploited. A proof-of-concept went public on August 11.…

CVE-2026-9198 lets attackers chain two Langflow API endpoints for unauthenticated RCE. CISA confirms active exploitation. See fixes and…
Critical unauthenticated RCE vulnerability CVE-2026-6875 hits ServiceNow via a GlideRecord sandbox escape. Attackers are already exploiting unpatched instances.
WP2Shell chains CVE-2026-60137 and CVE-2026-63030 for unauthenticated RCE on WordPress Core. Patch to 6.8.6, 6.9.5, or 7.0.2 now,…
CVE-2026-48282 is a critical ColdFusion RDS path traversal vulnerability under active exploitation. Learn the risks, IOCs, and how…
Langflow CVE-2026-33017 is under active exploitation. Attackers deploy Monero miners via unauthenticated RCE. Get IOCs, patch steps, and…
CVE-2026-42271 enables unauthenticated RCE in LiteLLM when chained with CVE-2026-48710. Learn wha is at risk and how to…
ShinyHunters now bypasses WAF rules to exploit Oracle PeopleSoft CVE-2026-35273. See the new attack chain, detection steps, and…
Critical Langflow vulnerability CVE-2025-3248 allows unauthenticated remote code execution, enabling attackers to fully compromise vulnerable servers.
CVE-2025-24813, an Apache Tomcat RCE flaw, is under active attack. PoC exploit availability boosts risks, enabling threat actors…
A critical vulnerability (CVE-2024-9264) in Grafana allows remote code execution, risking system commands and sensitive file access. Immediate…