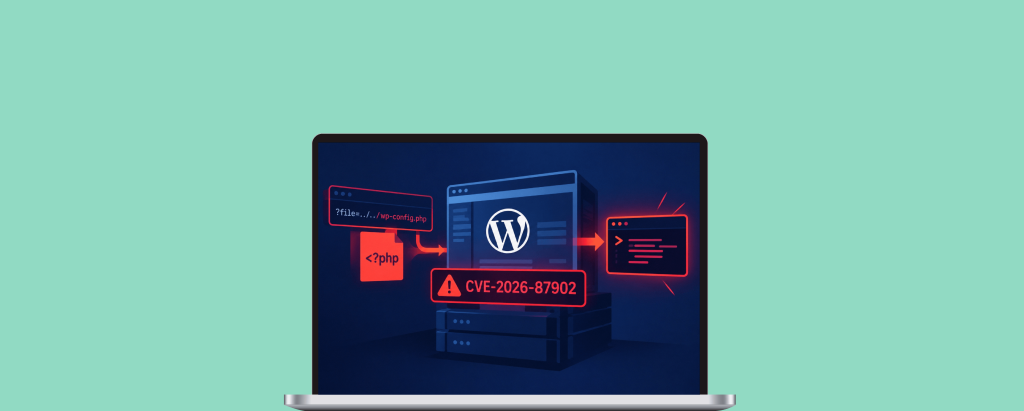
WordPress CVE-2026-87902: Unauthenticated RCE Exploited Within Hours
CVE-2026-87902 is a critical WordPress Core RCE flaw, exploited within hours of patch. See affected versions, exploitation flow,…
Real-time vulnerability analysis, threat intelligence, and expert insights to protect your web, API and AI agents from emerging attacks.
CVE-2026-87902 is a critical WordPress Core RCE flaw, exploited within hours of patch. See affected versions, exploitation flow,…
Next.js CVE-2026-94545 (CVSS 9.5) enables RCE through next/og SVG image generation. Learn affected versions, the Satori root cause,…
ShinyHunters now bypasses WAF rules to exploit Oracle PeopleSoft CVE-2026-35273. See the new attack chain, detection steps, and…
Quantum computers could very soon undermine the public-key cryptography that secures financial transactions, health records, and other sensitive…
cPanel disclosed a critical EmailTrack flaw letting standard mail accounts reach root access. Check affected versions, patch links,…
Manual pentesting samples your risk. Indusface WAS AI Pentest tests every endpoint, role, and workflow, with expert validation…

SwyftComply AI closes the vulnerability discovery-to-protection gap before attackers exploit it. Autonomous protection, expert-verified, audit-ready.
Critical Langflow RCE (CVE-2026-0768) is under active exploitation via the validate endpoint. Learn the impact, IOCs, and how…

CVE-2026-55040, a critical SharePoint authentication bypass, is now being actively exploited. A proof-of-concept went public on August 11.…

CVE-2026-9198 lets attackers chain two Langflow API endpoints for unauthenticated RCE. CISA confirms active exploitation. See fixes and…

CVE-2026-58048 lets low-privilege cPanel accounts escalate to root database access via a public PoC. Explore risk details and…
Oracle's largest-ever CPU patches critical unauthenticated flaws in PeopleSoft, WebLogic, and E-Business Suite. See AppTrana's coverage for each.