PHP2Shell (CVE-2026-109618 & CVE-2026-109619): Pre-Auth RCE in PHP Core Puts Web Servers at Risk
PHP2Shell abuses PHP’s session upload progress feature. Learn the signs of exploitation, php.ini hardening steps, and how AppTrana…
9 articles
PHP2Shell abuses PHP’s session upload progress feature. Learn the signs of exploitation, php.ini hardening steps, and how AppTrana…
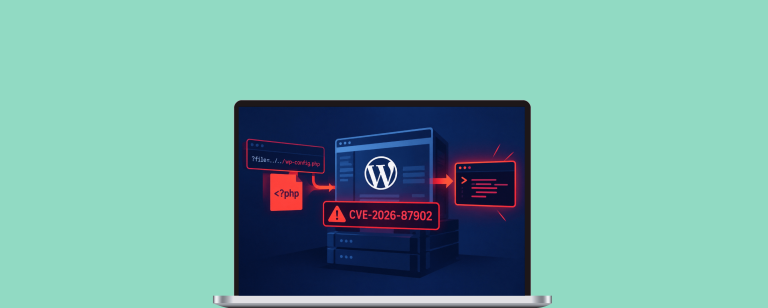
CVE-2026-87902 is a critical WordPress Core RCE flaw, exploited within hours of patch. See affected versions, exploitation flow,…
Next.js CVE-2026-94545 (CVSS 9.5) enables RCE through next/og SVG image generation. Learn affected versions, the Satori root cause,…
Oracle's largest-ever CPU patches critical unauthenticated flaws in PeopleSoft, WebLogic, and E-Business Suite. See AppTrana's coverage for each.
Learn how agencies secure Magento stores against exploits using virtual patching, WAF enforcement, & managed SOC support while…
Vulnerability management identifies and prioritizes security gaps, while patch management focuses on applying fixes to keep systems protected…
Uncover the secrets behind website hacking as we explore the methods employed by hackers to exploit vulnerabilities.
Sunil Agrawal (CISO, Glean) shared his experience on the sub-domain takeover and how it led him to build…
The race to patch known vulnerabilities bring forth an innovative approach called Virtual Patching. Learn what is virtual…